on 4 November, 2026
Texas Privacy Rules for Office Copiers in Finance and Healthcare
Texas law requires reasonable protection, proper destruction and fast breach notice for sensitive data, and copier hard drives hold plenty of it. Here is how ch. 521, HB 300 and the FTC Safeguards Rule apply.
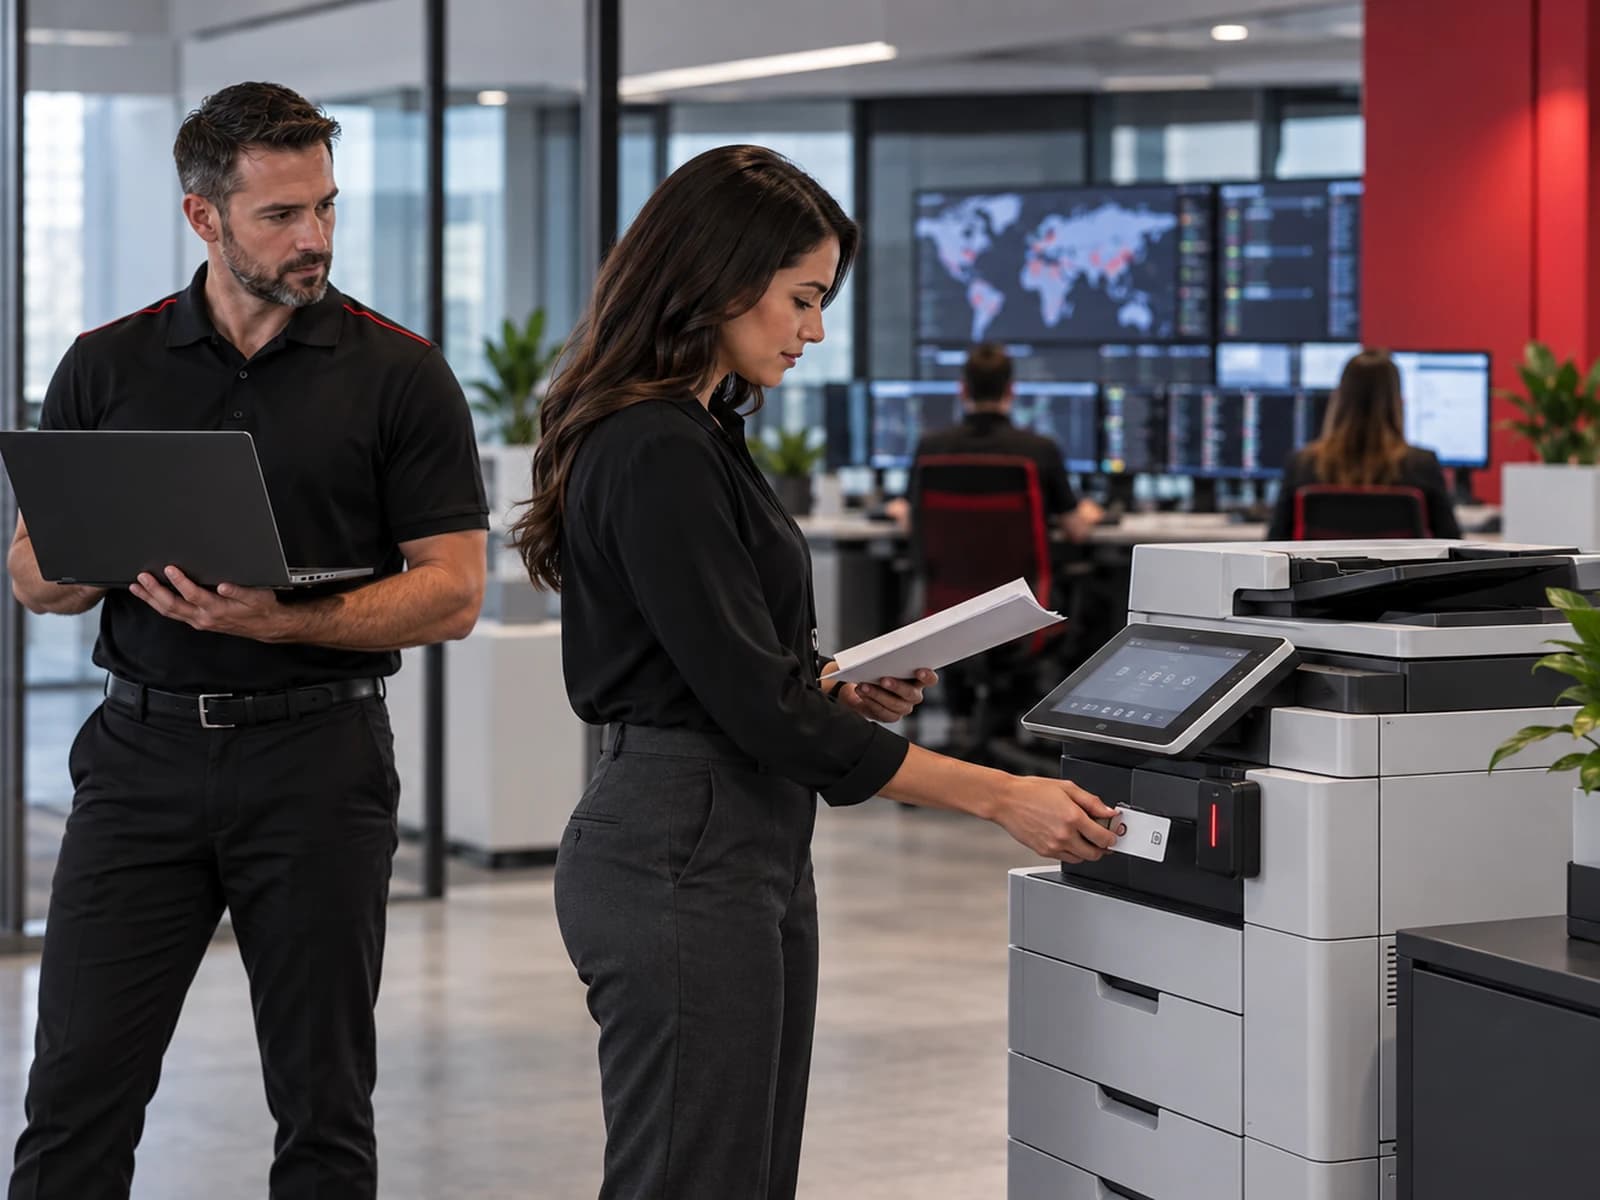
Texas businesses that copy, scan or fax customer and patient records have three sets of rules that reach the office copier: Texas Business and Commerce Code chapter 521 (reasonable security, record destruction and breach notice), Texas Health and Safety Code chapter 181 (Medical Records Privacy, often called the Texas Medical Records Privacy Act, as expanded by HB 300), and, for non-bank financial businesses, the FTC Safeguards Rule. All three matter at the copier because, as the Federal Trade Commission notes, a digital copier's hard drive stores data about the documents it copies, prints, scans, faxes or emails. This guide is for finance and healthcare offices in Dallas-Fort Worth and across Texas; it is general information, not legal advice, so confirm your obligations with counsel.
What does Texas Business and Commerce Code chapter 521 require?
Chapter 521, the Identity Theft Enforcement and Protection Act, protects "sensitive personal information." That term covers a person's name combined with a Social Security number, a driver's license or government ID number, or a financial account or card number with its access code, when those items are not encrypted. It also covers information that identifies a person and relates to their physical or mental health, their health care or payment for that care.
Section 521.052 sets two duties that apply directly to office equipment:
- Reasonable procedures. A business must implement and maintain reasonable procedures, including appropriate corrective action, to protect sensitive personal information it collects or maintains from unlawful use or disclosure.
- Destruction. A business must destroy, or arrange to destroy, customer records containing sensitive personal information that it will not retain, by shredding, erasing or otherwise making the information unreadable or indecipherable.
The statute does not name copiers, but erasing is one of the listed methods, and the FTC notes that simply deleting files or reformatting a copier drive does not actually remove the data. One exception matters for finance offices: section 521.052 does not apply to a financial institution as defined by the federal Gramm-Leach-Bliley Act. For non-bank financial businesses, the parallel security duty comes from the FTC Safeguards Rule, covered below.
How fast must a Texas business report a breach?
Section 521.053 applies to any person who conducts business in Texas and owns or licenses computerized sensitive personal information, with no financial institution exception.
| Who gets notice | Deadline | Trigger |
|---|---|---|
| Affected individuals | Without unreasonable delay, no later than 60 days after determining the breach occurred | Any breach of system security |
| Texas Attorney General | As soon as practicable, no later than 30 days after determining the breach occurred | At least 250 Texas residents affected |
| Nationwide consumer reporting agencies | Without unreasonable delay | More than 10,000 people notified at one time |
Since September 1, 2023, the Attorney General's report must be submitted electronically on the form on the Attorney General's website. The definition of a breach includes encrypted data if the person who accessed it also had the decryption key. Civil penalties range from $2,000 to $50,000 per violation, and failing to notify individuals can add up to $100 per person per day, capped at $250,000 for a single breach.
How does HB 300 change things for Texas healthcare offices?
HB 300, which took effect September 1, 2012, expanded chapter 181 of the Health and Safety Code. The result is a definition of "covered entity" that is broader than HIPAA's. It includes anyone who, whether for profit or on a nonprofit or pro bono basis, assembles, collects, analyzes, uses, evaluates, stores or transmits protected health information, and it names business associates, information or computer management entities, clinics, health care providers and website operators. It also includes anyone who comes into possession of protected health information, and the employees, agents and contractors of those entities.
That breadth is why a practice should ask counsel whether its vendors, including the company that services its copiers, fall inside the definition. Chapter 181 also adds requirements HIPAA does not spell out the same way:
- Training. Each covered entity must train employees on state and federal law concerning protected health information as it applies to their duties, within 90 days of hire, and again within a reasonable period (no later than one year) after a material change in the law. Each employee signs a statement of completion, which the entity keeps for six years.
- Electronic disclosure. A covered entity must give notice when protected health information is subject to electronic disclosure, and in general needs a separate authorization for each electronic disclosure, with exceptions for disclosures to other covered entities for treatment, payment, health care operations or insurance functions, or as other law permits.
- Penalties. The Attorney General can seek up to $5,000 per violation per year for negligent violations, $25,000 for knowing or intentional ones, $250,000 where information was used for financial gain, and up to $1.5 million a year for a pattern or practice.
Patient health information is also "sensitive personal information" under chapter 521, so that chapter's destruction rule and breach deadlines apply to healthcare offices on top of HIPAA.
Which Texas businesses fall under the FTC Safeguards Rule?
The Safeguards Rule (16 CFR Part 314) applies to financial institutions under FTC jurisdiction. The rule names mortgage lenders, payday lenders, finance companies, mortgage brokers, account servicers, check cashers, collection agencies, credit counselors and other financial advisors, tax preparation firms, and non-federally insured credit unions, among others. The FTC's guidance for auto dealers says dealers that finance or arrange financing are covered, as are dealers that lease vehicles for longer than 90 days.
Several of the rule's required safeguards land on a networked copier or MFP that stores and sends customer files:
- Inventory: identify and manage "the data, personnel, devices, systems, and facilities" the business relies on, a list that should include the copier fleet (314.4(c)(2)).
- Access controls: authenticate users and limit each person's access to the customer information they need (314.4(c)(1)).
- Encryption: encrypt all customer information at rest and in transit over external networks, or, where encryption is infeasible, use effective alternative compensating controls reviewed and approved by the business's Qualified Individual (314.4(c)(3)).
- Logging: monitor and log the activity of authorized users (314.4(c)(8)).
- Disposal: securely dispose of customer information no later than two years after it was last used for the customer, with limited exceptions (314.4(c)(6)).
- Service providers: select capable providers, require safeguards by contract and assess them periodically (314.4(f)).
Since May 13, 2024, the rule has also required notice to the FTC, through a form on the FTC's website, no later than 30 days after discovering a "notification event" involving at least 500 consumers. A notification event is the unauthorized acquisition of unencrypted customer information. Firms that keep customer information on fewer than 5,000 consumers are exempt from a few provisions (such as the written risk assessment and written incident response plan), but not from encryption, access control or disposal.
A copier checklist for Dallas-Fort Worth finance and healthcare offices
Whether the office is a mortgage broker in Dallas, a tax practice in Fort Worth or a clinic in Arlington, these steps address the copier side of all three rule sets.
- Inventory every copier, MFP, scanner and fax that stores customer or patient data, with model, serial number, location and whether it is owned or leased.
- Encrypt the drive and turn on overwrite. The FTC recommends both and suggests securely overwriting the entire drive at least once a month.
- Require login at the machine. Use badge or PIN authentication and secure release, so loan packages and patient records wait until the right person is at the copier.
- Keep and review job logs for scanning, printing and administrator access.
- Restrict scan-to-email to internal or encrypted destinations, and review the shared address book.
- Put data handling in the service contract. Spell out how technicians treat stored data, what happens to a replaced drive and how sanitization is confirmed.
- Erase before return or disposal. Check whether your lease says you keep the drive or the provider overwrites it, and keep a written record of sanitization tied to the serial number. Do not pull the drive yourself; the FTC warns that removing it without replacing its firmware can leave the machine inoperable.
- Train staff on the procedures, including the chapter 181 training clock for healthcare employees.
- Know your breach clocks: 30 days to the Texas Attorney General (250 or more Texans), 60 days to individuals, and 30 days to the FTC for Safeguards Rule notification events involving 500 or more consumers.
Talk to a local DEXpert
DEX Imaging serves Dallas-Fort Worth from our Dallas and Arlington offices, and the same rules apply for clients we support from our Houston, Austin and San Antonio offices. Our print security service covers drive encryption, secure overwrite and secure print release, and DEX Managed IT provides managed IT and cybersecurity for the rest of the network. When a machine is retired or returned, your DEX rep will ask whether you want its hard drive wiped, and DEX will wipe it for you if you do. See how DEX supports financial services and healthcare offices, or request a quote.
Frequently asked questions
Does Texas law require copier hard drives to be wiped?
Section 521.052 requires a business to destroy customer records containing sensitive personal information that it will not retain, by shredding, erasing or otherwise making them unreadable. It does not name copiers, but a drive holding scanned customer records should be erased before the machine leaves your control.
When must a Texas business notify the Attorney General of a breach?
No later than 30 days after determining the breach occurred, if it involves at least 250 Texas residents. The report is filed electronically on the Attorney General's website.
Are mortgage brokers and tax preparers covered by the FTC Safeguards Rule?
Yes. The rule names mortgage brokers and tax preparation firms among the financial institutions it covers, along with finance companies, collection agencies and others under FTC jurisdiction.
Does HB 300 apply if our practice already follows HIPAA?
Yes. Chapter 181 requires HIPAA covered entities to comply with HIPAA's privacy standards and also applies its own broader definition, training requirement and penalties.
Are small financial firms exempt from the Safeguards Rule?
Not entirely. Firms with customer information on fewer than 5,000 consumers are exempt from a few provisions, such as the written risk assessment and incident response plan, but must still meet the core safeguards, including encryption, access control and secure disposal.